> ## Documentation Index
> Fetch the complete documentation index at: https://gcore-doc-1894.mintlify.site/llms.txt
> Use this file to discover all available pages before exploring further.
# Specify HTTP methods allowed for content requests from the CDN
By default, a CDN resource accepts all standard HTTP methods. The **Enable HTTP methods** option restricts which methods the CDN accepts, returning `405 Method Not Allowed` for all others before the request reaches the origin.
To configure allowed HTTP methods:
1. Log in to the [Gcore Customer Portal](https://portal.gcore.com) and navigate to **CDN** > **CDN resources**.
2. Click the CNAME of the resource to open its settings.
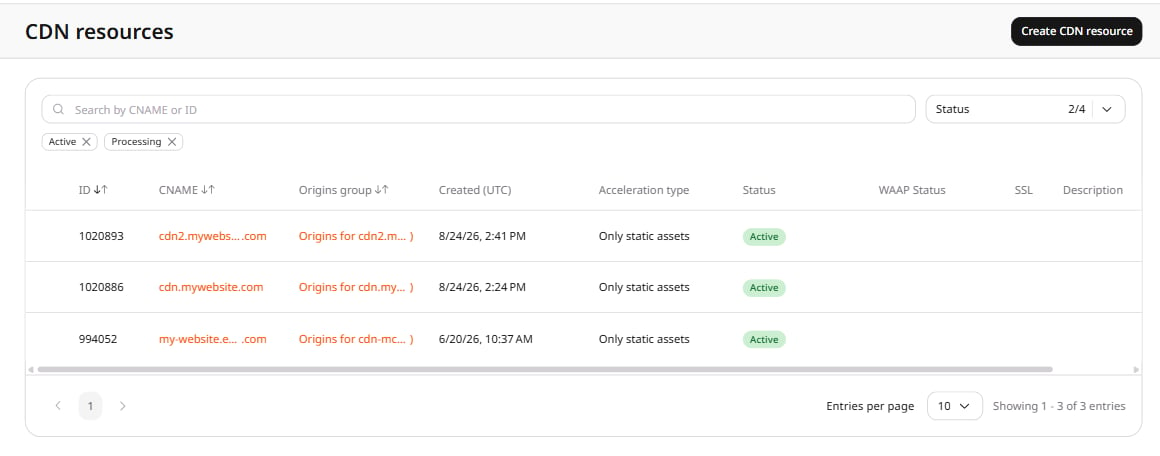 3. On the **OPTIONS** tab, scroll to **HTTP methods** and click the **Enable HTTP methods** toggle.
4. In the **Choose HTTP methods** field, add the methods the CDN should accept. Remove any method tag to block that method.
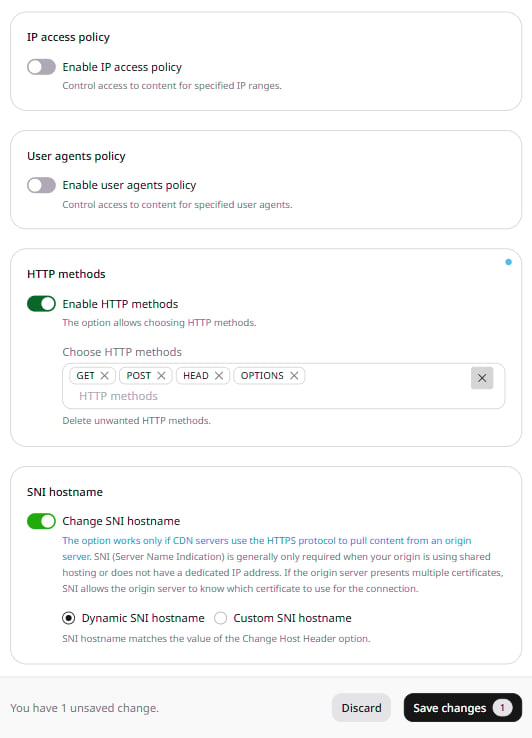 5. Click **Save changes**.
For most static content delivery, GET and HEAD are sufficient. Allow POST as well if the resource serves dynamic requests, form submissions, or API calls.
When a client sends a method that isn't allowed, the CDN returns `405 Method Not Allowed` without forwarding the request to the origin.